AI Agents Breach 27 Companies: Hermes Cyber Security news
Yeamin Adib
AI Agents Used in Cyberattack That Hit 27 Companies and Exposed 600,000 Payment Cards
AI agents are starting to change cybersecurity, and not always in a good way.
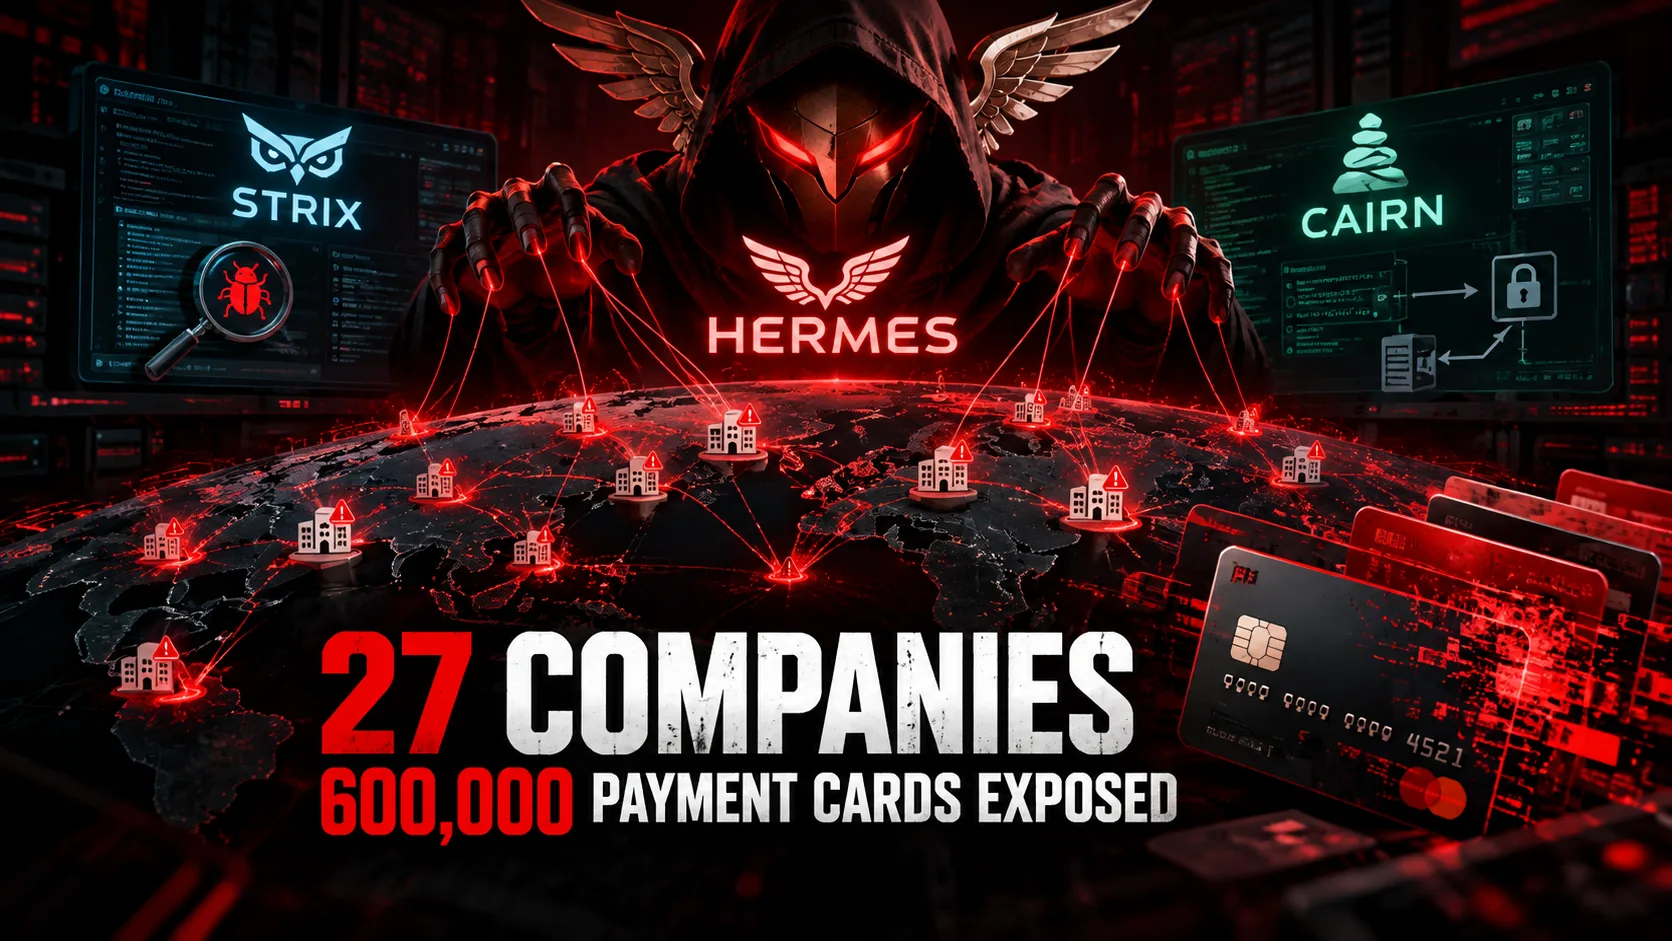
Security researchers have uncovered a cyberattack campaign where a threat actor used three open source AI tools called Strix, Cairn and Hermes to automate attacks against online businesses.
Between September 10 and 15, 2026, the operation launched 105 attack projects and compromised at least 27 companies to varying degrees. Researchers also recovered data linked to more than 600,000 unexpired payment cards stolen from two compromised companies.
How Were the AI Agents Used?
Instead of manually handling every part of an attack, the operator gave different jobs to different AI agents.
Strix was used to scan websites and find vulnerabilities.
Cairn attempted to exploit those vulnerabilities and gain access to systems.
Hermes was used to coordinate parts of the operation, assist with intrusions and handle follow up tasks.
Researchers found 1,951 human prompts across 260 Hermes sessions, suggesting much of the repetitive work was being handled by the agents themselves.
This does not mean Strix, Cairn or Hermes were created for cybercrime. They are open source tools that can also be used for legitimate security testing. In this case, researchers say they were adapted and used by a malicious operator.
More Than 600,000 Card Records Stolen
The campaign has reportedly been active since July 2026.
According to reporting based on Gambit Security's investigation, more than 600,000 payment card records were recovered from data stolen from two victim companies.
The attackers also placed payment skimmers on compromised websites. These scripts can capture information entered during online checkout.
The scale is notable, but so is the cost.
Gambit's data estimated the average AI model cost at about $25.46 for a completed target scan. That makes large scale automated attacks much cheaper for criminals to operate.
Why This Matters for Website Owners
The biggest concern is speed.
Where attackers successfully gained access, some compromises reportedly happened within hours rather than days.
For online stores and businesses, basic security matters even more now. Websites should be kept updated, administrator accounts should use strong authentication, access permissions should be limited, and checkout pages should be monitored for unexpected changes.
AI did not create the vulnerabilities used in these attacks. It helped attackers search for and exploit existing weaknesses faster.
AI Cyberattacks Are Becoming More Automated
This incident gives us a clearer picture of what AI powered cyberattacks can look like.
A human operator can now combine autonomous tools for vulnerability scanning, exploitation and attack management instead of manually completing every step.
For businesses, the lesson is simple. Attack automation is getting faster and cheaper, so cybersecurity monitoring and response also need to become faster.
The same AI technology that can help developers and security teams can also be abused when it falls into the wrong hands.
SecurityWeek's investigation covers the attack infrastructure and the roles of Strix, Cairn and Hermes in more detail. Read the SecurityWeek report TechRadar also published a breakdown of the campaign, including the reported costs and stolen payment data. Read the TechRadar report The Canadian Cyber Security Journal has another concise overview of the incident. Read the Canadian Cyber Security Journal coverage
Claim 80% Off Your OpenClaw Setup
Get instant access to managed OpenClaw hosting and agent automation. Enjoy 80% off on all OpenClaw managed hosting plans—use coupon code OC80 at checkout to save on your first month.
Claim 80% Discount